Learn
Learn
Plain explanations of the threats SphereTI monitors — what each one is, how it reaches an organisation, and what actually detects it.
Showing 1–9 of 14 articles
Dark-Web
Dark Web vs Deep Web: What's the Difference?
The author of the famous 96 percent figure has disowned it. What the measured numbers actually show.
Read
Deception
What Are Canary Tokens?
High precision detection bought with unknowable recall. The trade is worth understanding before you deploy any.
Read
Brand protection
What Is Business Email Compromise?
Most of it arrives from a Gmail account with the right name on it. There is no protocol that stops that.
Read
Credential theft
How Attackers Bypass MFA
Most MFA bypass does not attack MFA. It waits until the authentication is over and takes the result.
Read
Credential theft
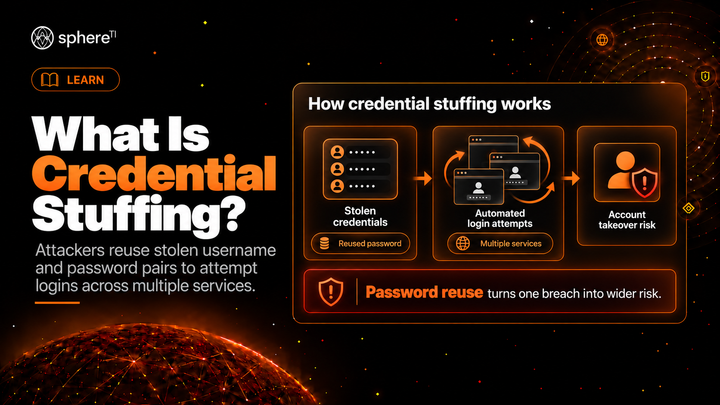
What Is Credential Stuffing?
One attempt against a million accounts, not a million attempts against one. That shape is why the usual defences miss it.
Read
Vulnerability intelligence
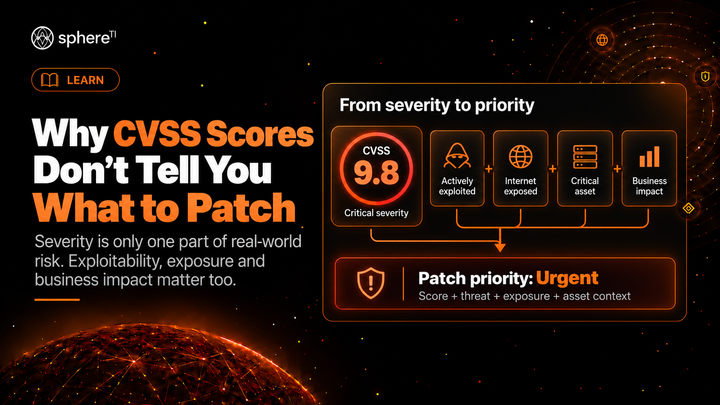
Why CVSS Scores Don't Tell You What to Patch
NIST stopped scoring every CVE in April 2026. What that tells you about severity-based triage.
Read
Dark-Web
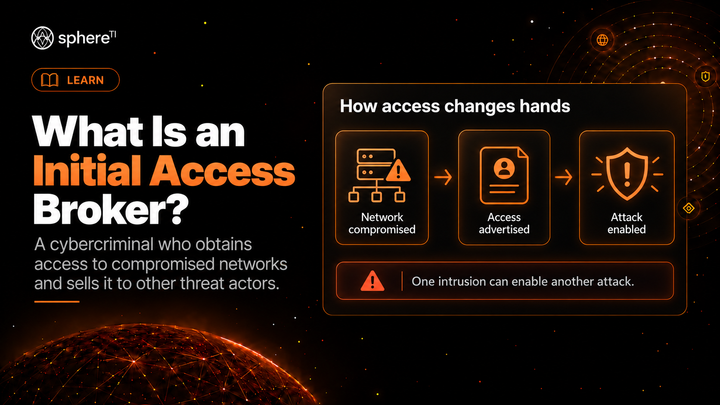
What Is an Initial Access Broker?
The intermediaries who turn a stolen password on a home laptop into a ransomware incident.
Read
Brand protection
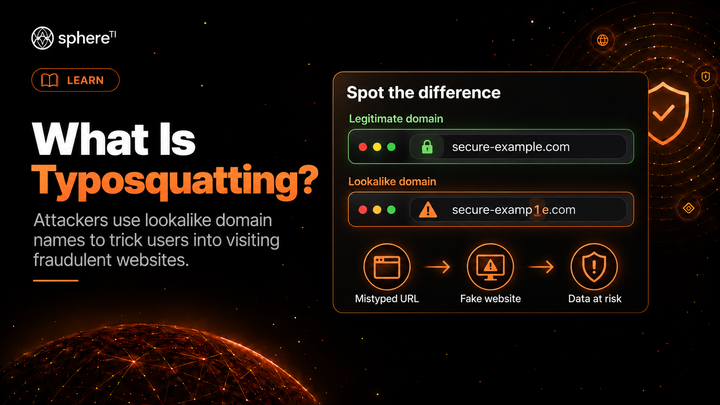
What Is Typosquatting?
Why the domain that impersonates you passes every email authentication check you have.
Read
Credential theft
What Is Session Cookie Theft?
The theft that survives a password reset, and why revocation is a separate action most teams skip.
Read